







Hybrid Cloud Architecture: Components and Deployment Models
- Hybrid cloud architecture connects on-premises, private cloud, and public cloud resources so they operate as one environment.
- Its core components are the environments, the connectivity between them, and five layers that span all of them.
- NIST defines four cloud deployment models, and hybrid binds two or more distinct infrastructures together.
- Common patterns include tiered hybrid, edge hybrid, business continuity, and cloud bursting, each with different security needs.
- Consistent identity and security policy across environments decides whether a hybrid architecture stays manageable and safe.
Hybrid cloud architecture is the design that connects an organization’s on-premises infrastructure, private cloud, and public cloud services so applications and data can run across them as one environment. It defines which workloads run where, how the environments connect, and which shared layers (identity, management, security, data, and observability) keep them consistent.
This article explains what hybrid cloud architecture is, its core components, a reference diagram, the deployment models and architecture patterns organizations use, how environments are integrated, the benefits and tradeoffs, three examples, and how to plan one. For the security design in depth, see Hybrid Cloud Security: Architecture and Best Practices.
What is hybrid cloud architecture?
Hybrid cloud architecture combines two or more distinct computing environments, typically on-premises or private infrastructure and public cloud, and binds them together so workloads and data can move between them.
NIST’s cloud computing definition, SP 800-145, describes hybrid cloud as a composition of two or more distinct cloud infrastructures (private, community, or public) that remain unique entities but are bound together by technology that enables data and application portability. In everyday usage, hybrid cloud also includes traditional data centers connected to public cloud, and increasingly edge sites such as plants, stores, and branches.
Hybrid is now the default for large organizations. Flexera’s 2026 State of the Cloud Report found that 73% of organizations run hybrid estates.
Core components of hybrid cloud architecture
Every hybrid cloud architecture has three kinds of components: the environments where workloads run, the connectivity between them, and the shared layers that span all of them.
| Component | What it does | Typical examples |
|---|---|---|
| On-premises data center | Runs legacy, regulated, latency-sensitive, or high-volume workloads | Virtualized servers, mainframes, storage arrays |
| Private cloud | Offers cloud-style self-service on dedicated infrastructure | Virtualization or container platforms run by the organization or a hosting provider |
| Public cloud (IaaS and PaaS) | Provides elastic compute, storage, and managed services | Hyperscaler infrastructure and platform services |
| SaaS applications | Delivers business applications as a service | Email, collaboration, CRM, HR systems |
| Edge sites | Processes data close to where it is produced | Plants, stores, clinics, branch offices |
| Connectivity | Links environments securely and reliably | Site-to-site VPN, private interconnects, SD-WAN, internet |
| Identity and access | Provides one source of identity across environments | Federated identity provider, MFA, workload identity |
| Management and orchestration | Deploys and operates workloads consistently | Infrastructure as code, Kubernetes, hybrid management platforms |
| Security | Enforces access, threat, and data policy everywhere | Secure web gateway, ZTNA, CASB, DLP, DSPM, segmentation |
| Data and integration | Moves and synchronizes data and services | Replication, backup, APIs, event streaming |
| Observability | Shows what is happening across environments | Logs, metrics, traces, SIEM |
Cloud providers also offer ways to run their services inside customer facilities. AWS Outposts extends AWS infrastructure and services to on-premises locations, and Azure Local, formerly Azure Stack HCI, runs on customer hardware and is managed through Azure Arc. These platforms make the on-premises side look more like the cloud, but they do not remove the need for shared identity, security, and observability layers.
Hybrid cloud architecture diagram
A hybrid cloud architecture diagram should show the environments, the connectivity between them, and the layers that span them all.
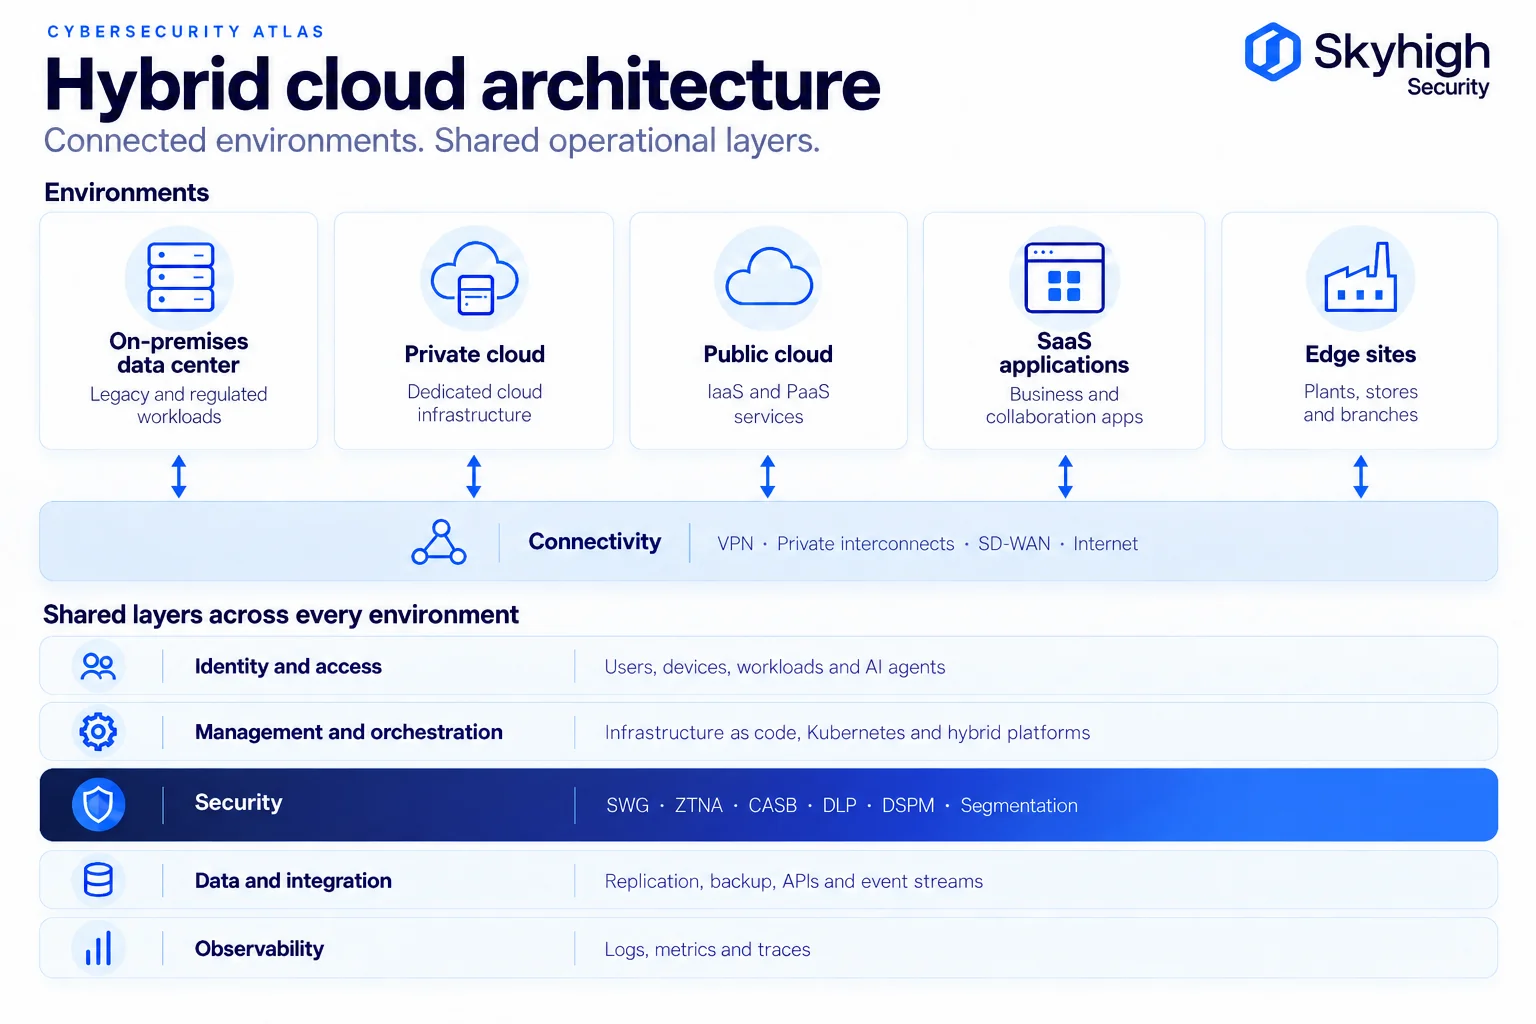
The top row shows where workloads run. The connectivity layer shows how those environments reach each other. The five layers below span every environment; if any of them is implemented separately in each environment, the architecture fragments. The security layer is where fragmentation is most expensive, because separate policies for each environment create gaps attackers can use. For the security-specific view, see the Hybrid Cloud Security Reference Architecture.
Hybrid cloud deployment models
NIST defines four cloud deployment models, and hybrid is the one that combines the others.
| Deployment model | Definition (NIST SP 800-145) | Typical use |
|---|---|---|
| Private cloud | Infrastructure provisioned for exclusive use by one organization | Regulated or highly customized workloads |
| Community cloud | Infrastructure shared by a specific community with common concerns | Government or industry consortiums |
| Public cloud | Infrastructure provisioned for open use by the general public | Elastic and managed services |
| Hybrid cloud | Two or more distinct infrastructures bound together for data and application portability | Most enterprises |
In practice, organizations build hybrid architectures in four common configurations:
- Data center plus public cloud: existing on-premises systems connected to one hyperscaler.
- Private cloud plus public cloud: a modernized internal platform connected to public cloud services.
- Hybrid with edge: central data center and cloud, plus local processing at plants, stores, or branches.
- Hybrid multi-cloud: on-premises infrastructure connected to more than one public cloud provider. See Hybrid Cloud vs. Multi-Cloud Security.
Common hybrid cloud architecture patterns
Hybrid architecture patterns describe how workloads are split or duplicated across environments, and each pattern creates different security requirements.
Google’s Cloud Architecture Center groups hybrid and multicloud architecture patterns into distributed patterns, where parts of the system run in different environments, and redundant patterns, where the same system is duplicated across environments.
| Pattern | How it works | Security consideration |
|---|---|---|
| Tiered hybrid | Customer-facing tiers run in the cloud; back-end systems stay on premises | Protect and inspect the API and data paths between tiers |
| Partitioned multicloud | Different workloads or components run in different public clouds | Keep identity and policy consistent across providers |
| Analytics hybrid | Transactional systems stay on premises; analytics runs in the cloud | Classify and minimize data before it leaves |
| Edge hybrid | Time- or business-critical workloads run locally; the cloud handles the rest | Local enforcement that keeps working when the link is down |
| Environment hybrid | Development and test run in one environment, production in another | Sanitize test data and apply the same controls in both |
| Business continuity | A second environment serves as the recovery site | Replicate security policy and keys along with the data |
| Cloud bursting | Extra capacity comes from the cloud during demand peaks | Policy must follow workloads automatically as they scale |
Most organizations use several patterns at once, which is why a single, environment-independent security layer matters.

Hybrid cloud integration architecture
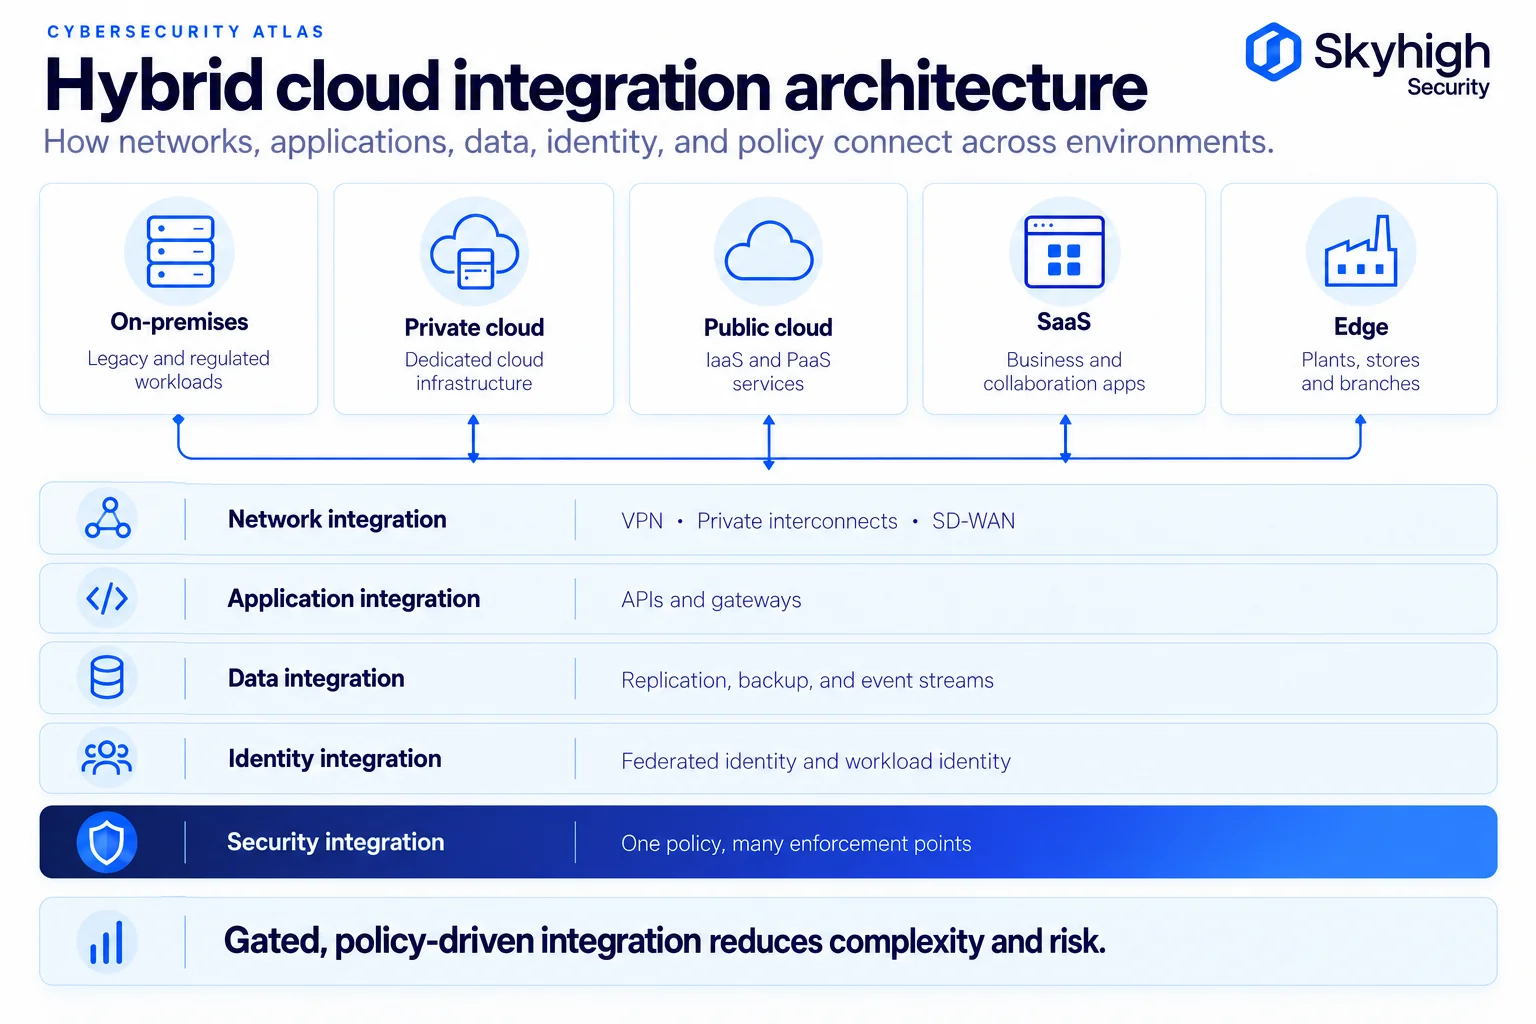
Hybrid cloud integration architecture defines how networks, applications, data, and identity connect across environments.
Network integration. Google’s secure networking patterns for hybrid and multicloud describe several approaches: mirrored networks for development and test, meshed networks in which all systems can communicate, gated patterns in which only selected APIs are exposed through gateways in one or both directions, and handover patterns in which on-premises systems pass data to cloud services without broad network connectivity. Gated patterns follow least privilege most closely and are usually the safer default.
Application integration. APIs, published through API gateways, give each environment a controlled interface instead of direct access to back-end systems.
Data integration. Replication, backup, batch transfers, and event streaming keep data synchronized. Each flow should be classified, encrypted, and logged.
Identity integration. One identity provider federated to every environment, with workload identities for services and AI agents, prevents separate identity silos from forming.
Security integration. Access, threat, and data policy should be defined once and enforced in every environment. NIST’s zero trust guidance, SP 800-207, separates the policy decision point from policy enforcement points, which is the model that makes this possible across environments.
Benefits and tradeoffs of hybrid cloud architecture
Hybrid cloud architecture gives organizations flexibility and control, but it adds complexity that has to be managed deliberately.
Benefits
- Workload placement by need: run each workload where latency, cost, regulation, and performance fit best.
- Control over sensitive data: keep regulated data and its processing on premises while using cloud services elsewhere.
- Gradual modernization: migrate applications in phases instead of all at once.
- Resilience: use a second environment for recovery, and keep local operations running during cloud or WAN outages.
- Elastic capacity: add cloud capacity for peaks without overbuilding the data center.
- Low latency at the edge: process data close to where it is produced.
Tradeoffs
- Operational complexity: more environments, tools, and skills to manage.
- Policy consistency: identity, security, and configuration drift when each environment is managed separately.
- Visibility gaps: logs and inventories spread across tools.
- Network and transfer costs: data movement between environments can be expensive.
- Higher breach impact when unmanaged: IBM’s Cost of a Data Breach Report 2025 found that breaches involving data across multiple environments averaged USD 5.05 million and took 276 days to identify and contain, the highest of any storage configuration.
Hybrid cloud architecture examples
The same components combine differently depending on the business, as these three examples show.
Example 1: Tiered hybrid for a bank
Online and mobile banking front ends run in the public cloud for elasticity. Core banking systems stay in the bank’s data centers. The front ends reach the core only through an API gateway, and traffic between tiers is inspected on bank-controlled infrastructure. Employees use SaaS collaboration tools under the same identity and data policies as internal systems.
Example 2: Edge hybrid for a manufacturer
Each plant runs production systems locally so operations continue if the WAN fails. Sensor data is summarized at the edge and sent to cloud analytics. Operational technology networks are segmented from corporate IT, and remote engineering access goes through per-application zero trust access rather than VPN.
Example 3: Business continuity for a health system
Clinical systems run in the health system’s data centers, with a recovery environment in the public cloud. Data, encryption keys, and security policy are replicated together, and failover is tested on a schedule so the recovery site is protected as well as the primary site.
Security considerations for hybrid cloud architecture
Security in a hybrid architecture works when it is designed as one layer across every environment rather than a set of separate controls for each.
- Identity first: one identity provider, phishing-resistant MFA, and governance for service accounts and AI agents.
- One policy, many enforcement points: define access, threat, and data rules once and enforce them in the data center, branches, cloud, and on devices.
- Deliberate inspection placement: decide where traffic is decrypted for each path. See Local vs. Cloud TLS Inspection.
- Data protection that follows the data: classify once and apply DLP across web, SaaS, private apps, endpoints, and AI tools. See DLP Across Cloud and On-Premises Environments.
- Residency and sovereignty: know which country inspection, logs, and keys sit in, and who operates and can be compelled to access that infrastructure. See Data Sovereignty in Hybrid Cloud Security.
- Shared responsibility clarity: the NSA and CISA Top Ten Cloud Security Mitigation Strategies include a dedicated strategy for hybrid and multi-cloud complexity.
Skyhigh Hybrid SSE Mesh applies this model to user access and data protection, with on-premises and cloud enforcement governed by one console and policy engine.
How to plan a hybrid cloud architecture
Planning a hybrid cloud architecture starts with workloads and data, not with infrastructure choices.
- Inventory workloads and data. Record each application’s dependencies, data sensitivity, latency needs, and regulatory constraints.
- Decide placement per workload. Choose on premises, private cloud, public cloud, SaaS, or edge based on that inventory.
- Choose patterns. Match workloads to patterns such as tiered hybrid, edge hybrid, or business continuity.
- Design connectivity and integration. Prefer gated network patterns and API-based integration over flat connectivity.
- Unify identity. Federate one identity provider to every environment before migrating workloads.
- Design one security and policy layer. Define policy once and plan enforcement points for every environment. See the Hybrid Cloud Security Reference Architecture.
- Plan observability. Centralize logs and metrics while respecting residency rules.
- Plan for failure. Define recovery sites, failover behavior, and test schedules. See Hybrid SSE Resilience.
- Migrate in phases. Move workloads in waves with rollback plans, and retire legacy components deliberately.
Sources
- NIST. SP 800-145: The NIST Definition of Cloud Computing (September 2011). https://csrc.nist.gov/pubs/sp/800/145/final
- Flexera. 2026 State of the Cloud Report. https://info.flexera.com/CM-REPORT-State-of-the-Cloud
- Google Cloud. Hybrid and multicloud architecture patterns, Cloud Architecture Center. https://docs.cloud.google.com/architecture/hybrid-multicloud-patterns-and-practices
- Google Cloud. Hybrid and multicloud secure networking architecture patterns, Cloud Architecture Center. https://docs.cloud.google.com/architecture/hybrid-multicloud-secure-networking-patterns
- Google Cloud. Build hybrid and multicloud architectures using Google Cloud, Cloud Architecture Center. https://docs.cloud.google.com/architecture/hybrid-multicloud-patterns
- AWS. AWS Outposts. https://aws.amazon.com/outposts/
- Microsoft. Azure Local documentation. https://learn.microsoft.com/en-us/azure/azure-local/
- Microsoft. Azure Arc overview. https://learn.microsoft.com/en-us/azure/azure-arc/overview
- NIST. SP 800-207: Zero Trust Architecture (August 2020). https://csrc.nist.gov/pubs/sp/800/207/final
- IBM and Ponemon Institute. Cost of a Data Breach Report 2025. https://www-api.ibm.com/adobe/assets/urn:aaid:aem:607b9590-38e0-4c91-b433-aa8a17f5b5e8/original/as/cost-of-a-data-breach-2025-full-report.pdf
- NSA and CISA. Top Ten Cloud Security Mitigation Strategies (March 7, 2024). https://www.nsa.gov/Press-Room/Press-Releases-Statements/Press-Release-View/Article/3699169/nsa-releases-top-ten-cloud-security-mitigation-strategies/