







How the Blue Coat Modernization Program Works
- Skyhigh's Blue Coat Modernization Program moves Symantec Edge SWG and ASG customers to Skyhigh Hybrid SSE Mesh.
- A commercial offset applies remaining Broadcom investment toward the transition, paired with services-backed migration.
- Deployment stays your choice: on premises, hybrid, or cloud, with no forced move to the cloud.
- Skyhigh appliances run alongside existing gateways so CPL policy is validated before any cutover.
- With the SGOS 7.3 window closing in December 2026, confirm eligibility, scope, and timing now.
Blue Coat modernization is the process of replacing Broadcom’s Symantec Edge SWG (formerly Blue Coat ProxySG) and ASG appliances with a current secure web gateway and, optionally, a broader Security Service Edge platform. Skyhigh’s Blue Coat Modernization Program supports that transition with a commercial offset, a structured assessment, and a phased, services-backed migration to Skyhigh Hybrid SSE Mesh.
Leaving a secure web gateway is usually held back by two concerns: cost and disruption. The program is designed to address both.
Who the program is for
The program is aimed at organizations running Blue Coat, Symantec, or Broadcom web security appliances that face one or more of these triggers:
- End-of-life pressure. Broadcom set December 31, 2024 as the SGOS 7.3 end-of-life announcement date, with no new features after that date and two years to upgrade to SGOS 7.4 (Broadcom). Hardware end-of-life dates vary by appliance model.
- A forced tooling change. SGOS 7.4 removes the Java Management Console and Java Visual Policy Manager (Broadcom), so staying on Blue Coat still means re-learning how policy is managed.
- Retired on-premises components. On-premises Web Isolation reached end of life on January 1, 2024 (Broadcom).
- Renewal and licensing friction. Separate consoles and SKUs for Edge SWG, Cloud SWG, and Symantec DLP, and rising maintenance costs.
- New requirements. AI tools and agents operating inside the network over persistent WebSocket connections benefit from zero trust enforcement at the site.
What the program includes
The program combines a commercial offset, an assessment, policy carry-forward, deployment flexibility, a path to full SSE, and consumption-based licensing.
A commercial offset. Skyhigh’s commercial offset program applies remaining Broadcom investment toward the modernization, so the budget that would have funded another appliance refresh funds the transition instead (Skyhigh Security). An advisor sizes the offset for your estate and timing.
A modernization assessment. Skyhigh’s assessment covers:
- An inventory of existing CPL policies and data sovereignty requirements
- A hybrid deployment plan with parallel cutover designed to minimise disruption to current operations
- A commercial offset estimate for remaining Broadcom investment
Policy carry-forward. Existing CPL policies are re-expressed in Skyhigh’s unified policy console through a validated import process, so teams start from their current policy state.
Deployment flexibility. Skyhigh SWG runs on premises, hybrid, or in the cloud. On-premises ProxySG estates can be replaced with on-premises Skyhigh appliances and extended to the cloud later, or not at all.
A path to full SSE. The same platform extends to CASB, DLP, ZTNA, Secure Browser Controls, DSPM, and remote browser isolation without adding another console.
Consumption-based licensing. Capabilities such as local ZTNA and Secure Browser Controls can be activated through a token-based model when needed.
How the migration works
Skyhigh’s modernization path runs in four phases, alongside existing Symantec Edge SWG infrastructure (Skyhigh Security):
- Assess and plan. Inventory CPL policies. Map data sovereignty zones, OT/SCADA environments, and SSL inspection performance. Identify rules to preserve and extend.
- Deploy in parallel. Deploy Skyhigh SWG appliances next to existing gateways. Import and validate CPL policy baselines. Run parallel traffic without disrupting production, and prepare and test rollback before production cutover.
- Adopt unified capabilities. Enable local ZTNA and agentless Secure Browser Controls. Extend with cloud CASB, DSPM, and DLP. Move users in controlled waves and retire legacy appliances after acceptance and the rollback window closes.
- Rationalize and optimize. Adjust token consumption, retire unused Broadcom entitlements, and continuously refine policy as code under one console.
Skyhigh reports that most organizations run phases two and three in parallel over six to twelve months. For a detailed checklist, see Secure Web Gateway Migration: Cutover and Rollback Checklist.

Requirements to confirm
Before committing, confirm eligibility, offset terms, scope, deployment model, policy import, integrations, timeline, and compliance with your Skyhigh advisor:
- Eligibility. Which Broadcom products, contracts, and remaining terms qualify for the offset
- Offset terms. How the offset is calculated and applied, and over what period
- Scope. Which sites, appliances, and user populations are included in the plan
- Deployment model. On-premises, hybrid, or cloud for each site, and hardware, virtual, or containerized appliances
- Policy import. Which CPL constructs are carried forward automatically and which need manual review
- Integrations. Authentication realms, SIEM and reporting, and how existing ICAP and DLP flows are re-expressed using Skyhigh cloud-applied data protection
- Timeline. How the plan aligns with your SGOS 7.3 support window and hardware end-of-life dates
- Coverage during transition. How your current Broadcom deployment remains supported while the parallel run is under way
- Compliance. Required certifications and authorizations for your sector and regions
Support to confirm
Confirm who supports each phase of the transition and what your own team is expected to do.
- Named contacts for assessment, deployment, and cutover
- Professional services included, and what your team is expected to do
- Support during parallel run and each cutover wave
- Training for administrators moving from CPL and VPM
- Escalation path and response times after go-live
Why plan now
Broadcom’s upgrade window for SGOS 7.3 closes at the end of December 2026.
Whether you upgrade to SGOS 7.4 or modernize, the Java console and VPM workflow change is unavoidable, so the policy rework cost exists either way. Starting an assessment now gives you a documented plan, an offset estimate, and a parallel deployment option before year-end decisions on renewals and support. See Blue Coat and ProxySG End of Life: Migration Planning for dates and options.
What you are moving to
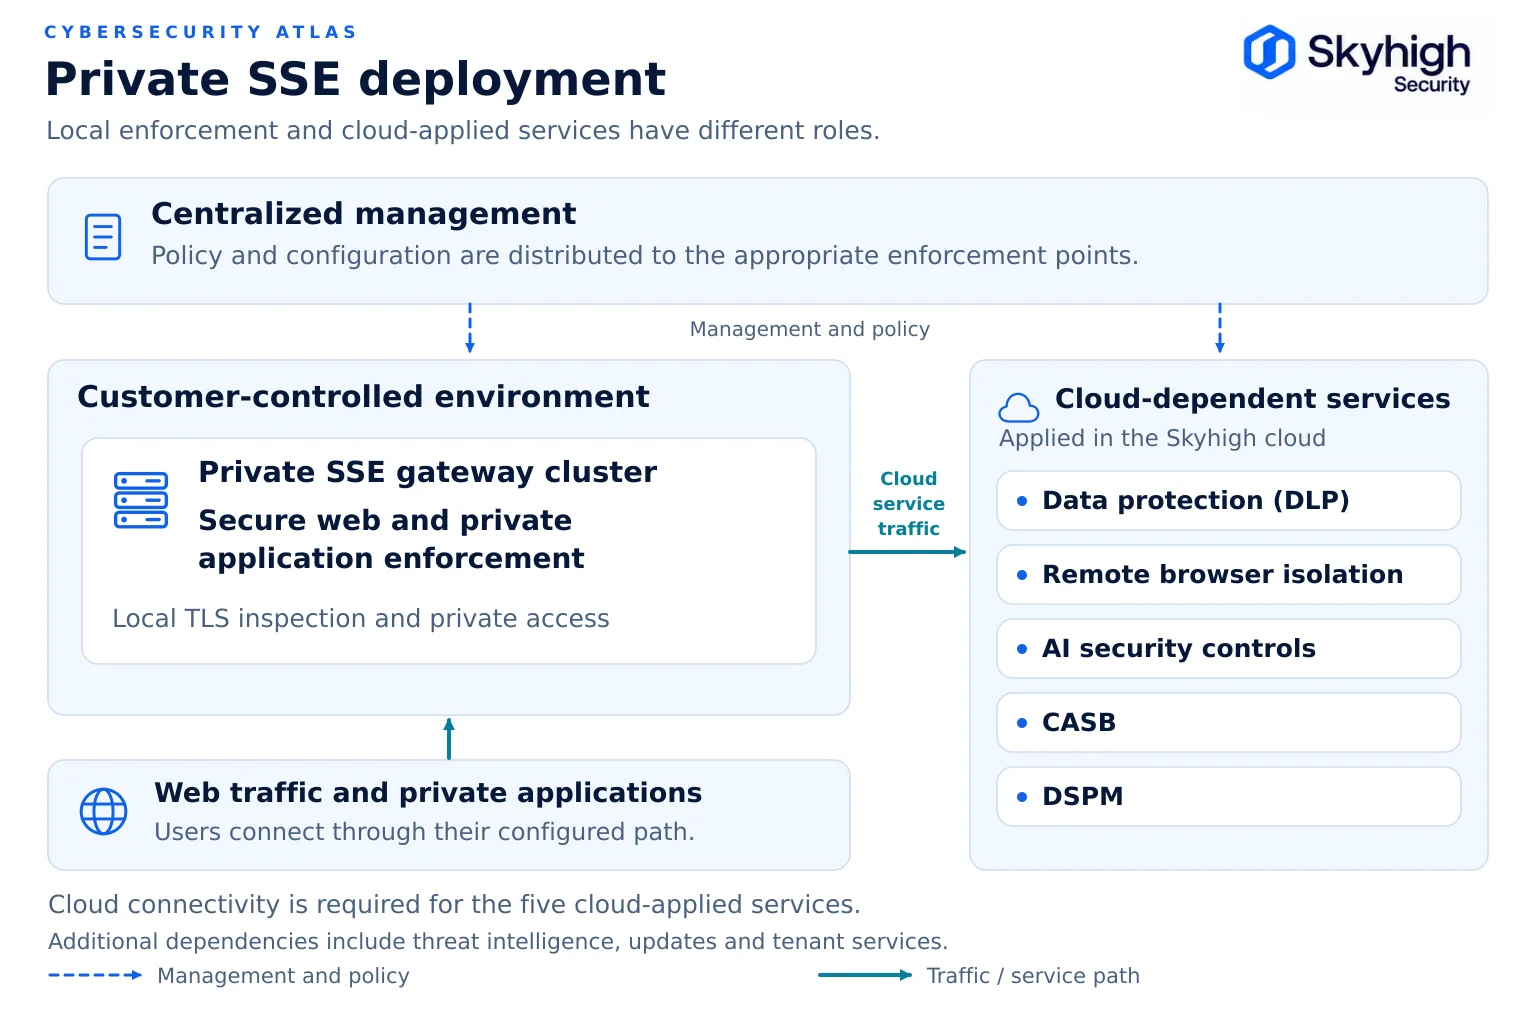
Skyhigh Hybrid SSE Mesh unifies on-premises SWG appliances, local ZTNA, and Secure Browser Controls with cloud CASB, DSPM, DLP, and RBI under one console and policy engine.
TLS decryption and web inspection can run locally on the Secure Service Gateway. Where data protection, isolation, or AI controls apply, the gateway forwards that traffic to the Skyhigh cloud, where the same policy is applied. Skyhigh was ranked first in the Advanced SSE Use Case in the 2026 Gartner® Critical Capabilities for Security Service Edge. Skyhigh reports that it is used by more than 3,000 organizations, including 80 percent of top global banks and 25 percent of the Fortune 500.
Plan your next step
Four steps move you from evaluation to a documented modernization plan.
- Confirm your SGOS versions and appliance models against Broadcom’s lifecycle article.
- Export and document current CPL and VPM policy.
- Identify sites with sovereignty, OT, or resilience requirements that need local enforcement.
- Request a modernization assessment to receive a policy inventory, hybrid deployment plan, and offset estimate. Skyhigh commits to a response from a specialist within one business day.
Still comparing options? See Blue Coat Alternatives and ProxySG Replacement.
Sources
- Broadcom. End of life and product lifecycle for Edge SWG (ProxySG) and Advanced Secure Gateway (KB 151102). https://knowledge.broadcom.com/external/article/151102/end-of-life-and-product-lifecycle-for-pr.html
- Broadcom. Switch to the Edge SWG (ProxySG) Admin Console (SGAC) (KB 251426). https://knowledge.broadcom.com/external/article/251426/switch-to-the-edge-swg-proxysg-admin-con.html
- Broadcom. Web Isolation On-premises EOL FAQ (KB 215429). https://knowledge.broadcom.com/external/article/215429/web-isolation-onpremises-eol-faq.html
- Skyhigh Security. Modernize Symantec Edge SWG (Blue Coat). https://www.skyhighsecurity.com/bluecoat-modernize.html
- Skyhigh Security. “Modernizing Your Symantec Edge Secure Web Gateway With Skyhigh Hybrid SSE Mesh” (July 15, 2026). https://www.skyhighsecurity.com/industry-perspectives/modernizing-your-symantec-edge-secure-web-gateway-with-skyhigh-hybrid-sse-mesh.html
- Skyhigh Security. “Skyhigh Security Ranked #1 in Advanced SSE Use Case in 2026 Gartner Critical Capabilities for Security Service Edge” (August 5, 2026). https://www.globenewswire.com/news-release/2026/08/05/3339504/0/en/skyhigh-security-ranked-1-in-advanced-sse-use-case-in-2026-gartner-critical-capabilities-for-security-service-edge.html
GARTNER is a registered trademark and service mark of Gartner, Inc. and/or its affiliates in the U.S. and internationally and is used herein with permission. All rights reserved. Gartner does not endorse any vendor, product or service depicted in its research publications.