







Blue Coat Alternatives and ProxySG Replacement
- Blue Coat ProxySG, Symantec ProxySG, and Broadcom Edge SWG are one product line under three owners.
- Broadcom's SGOS 7.3 upgrade window closes at the end of December 2026.
- Upgrading to SGOS 7.4 removes the Java console and VPM, so policy workflow changes either way.
- Require inline threat inspection, built-in DLP, modern protocols, one console, and flexible deployment.
- A hybrid gateway keeps local enforcement where required and extends the same policy to the cloud later.
A Blue Coat alternative is a secure web gateway (SWG) that replaces Broadcom’s Symantec Edge SWG, formerly Blue Coat ProxySG, including Advanced Secure Gateway (ASG) deployments. The capabilities that most separate a modern replacement from ProxySG are real-time inline threat inspection, integrated data loss prevention, a converged console, and flexible on-premises, hybrid, and cloud deployment. Skyhigh Hybrid SSE Mesh provides all four, with a guided transition through the Blue Coat Modernization Program.
Teams evaluating a ProxySG replacement are usually past the question of whether to switch. End of life, renewal cost, support friction, or roadmap concerns have made that call. The open question is what to replace ProxySG with, and how to do it without disrupting production.
Why teams replace Blue Coat ProxySG
Teams replace ProxySG because of a lifecycle deadline, a forced tooling change, retired on-premises components, console sprawl, and new AI-era traffic.
A lifecycle deadline. Broadcom set the SGOS 7.3 end-of-life announcement date as December 31, 2024. According to Broadcom’s lifecycle article, no new features are delivered on 7.3 after that date, limited support covers critical and high security fixes, and customers have two years from the announcement to upgrade to SGOS 7.4. That window closes at the end of December 2026. See Blue Coat and ProxySG End of Life: Migration Planning.
A forced tooling change. In SGOS 7.4, the Java-based Management Console and Java VPM are removed, and administrators move to the Edge SWG Admin Console, per Broadcom’s guidance. Staying on Blue Coat still means re-learning how policy is managed.
Components retired on premises. Broadcom ended support for all versions of on-premises Web Isolation on January 1, 2024, and now offers browser isolation only as a cloud service (Broadcom). Organizations that chose on-premises deployment for sovereignty reasons have fewer local options on the Broadcom platform.
Console and licensing sprawl. Full web, data, and cloud security on the Broadcom platform involves separate consoles for Edge SWG, Cloud SWG, and Symantec DLP, each with its own policy engine and renewal cycle. Policy drift between them creates audit exposure.
Support and focus. ProxySG is one product inside a large semiconductor and infrastructure software portfolio. Many customers report difficulty with support, maintenance, and renewal processes.
New traffic ProxySG was not designed for. AI tools and autonomous agents increasingly use persistent WebSocket connections and operate inside the network, where cloud-only inspection cannot reach and legacy proxies were not designed to inspect.
What to require in a ProxySG replacement
A ProxySG replacement should inspect inline in real time, build in data protection, support current protocols, and converge management into one console.
- Real-time inline threat inspection. Inline anti-malware at the gateway, with documented sandboxing location and verdict handling.
- Built-in data protection. Data protection applied through the vendor cloud under one policy, sharing classification with SaaS, endpoint, and AI tool controls, so content requiring inspection is forwarded from the on-premises gateway rather than handed to a separate ICAP-connected product.
- Current protocols. HTTP/2, TLS 1.3, and WebSocket-aware inspection.
- One console, one policy engine. Converged management across web, cloud, and private access.
- Deployment choice. On premises, hybrid, and cloud, with the same policy in each, so you control the timeline.
- Local control where required. On-premises TLS inspection and logging for sovereignty-bound or regulated traffic.
- A defined migration path. A services-backed method for carrying policy forward and running in parallel before cutover.
- A path to full SSE. The same platform should extend to CASB, ZTNA, DSPM, and remote browser isolation, so a gateway swap is not a dead end.
Three kinds of Blue Coat alternative
Blue Coat alternatives fall into three shapes, and the right one depends on how much change your environment can absorb.
Appliance-for-appliance refresh. Swap ProxySG for another on-premises proxy. This involves the least process change, but it keeps you tied to hardware cycles and can leave you managing a separate cloud product for remote users.
Cloud-only SSE. Move all web inspection to a cloud service. This offers maximum outsourcing of infrastructure, but it is a large cutover for teams with deep on-premises policy, and it moves decryption of all traffic to the vendor’s cloud. That may not be acceptable for regulated data or OT environments, and cloud-only enforcement cannot see traffic that never leaves the building.
Hybrid SWG. Keep on-premises enforcement where compliance, performance, or resilience require it, and extend the same policy to the cloud when ready. For most ProxySG estates, this is the pragmatic middle path. See Cloud vs. On-Premises Secure Web Gateways.
Symantec Edge SWG (Blue Coat) vs. Skyhigh Security
The clearest differences are the software path, console count, on-premises capabilities, and built-in data protection.
| Area | Broadcom Symantec Edge SWG (Blue Coat) | Skyhigh Hybrid SSE Mesh |
|---|---|---|
| Current software path | SGOS 7.3 limited support ends December 2026; move to SGOS 7.4 required | Continuously updated platform; on-premises, hybrid, and cloud |
| Management | Java console removed in 7.4; separate consoles for Edge SWG, Cloud SWG, and DLP | Single console and policy engine across SWG, CASB, DLP, ZTNA, RBI, and DSPM |
| Browser isolation | On-premises Web Isolation end of life January 1, 2024 | Remote browser isolation applied through the Skyhigh cloud |
| Zero-day protection | Relies on separate analysis components | Gateway Anti-Malware on the gateway; emulation sandboxing through the Skyhigh cloud |
| Data protection | Separate Symantec DLP product | Integrated cloud-applied DLP across supported channels |
| Private application access on premises | Confirm private-access components and on-premises enforcement support for the selected Broadcom deployment | Local ZTNA on on-premises and branch gateways |
| Browser and AI controls | Confirm browser and AI controls for the selected Broadcom components | Agentless Secure Browser Controls with WebSocket-aware inspection |
| Policy carry-forward | Rework required when moving to Admin Console | CPL policies re-expressed in Skyhigh’s policy console through a validated import process |
Why modernize in 2026
Three pressures make 2026 the natural year to modernize:
- The lifecycle deadline. The SGOS 7.3 upgrade window closes at the end of December 2026.
- The AI security gap. AI agents and AI tools operating inside the network need zero trust enforcement at the local network edge, which neither a legacy proxy nor a cloud-only service provides.
- Cost and complexity. Separate consoles, SKUs, and renewal cycles raise total cost of ownership, and per-user, per-module pricing charges the same whether a capability is used daily or rarely.
Because the move to SGOS 7.4 already forces a console and policy-workflow change, the rework cost exists whether you stay or switch. That makes this the natural point to evaluate alternatives.

Why enterprises choose Skyhigh as their Blue Coat alternative
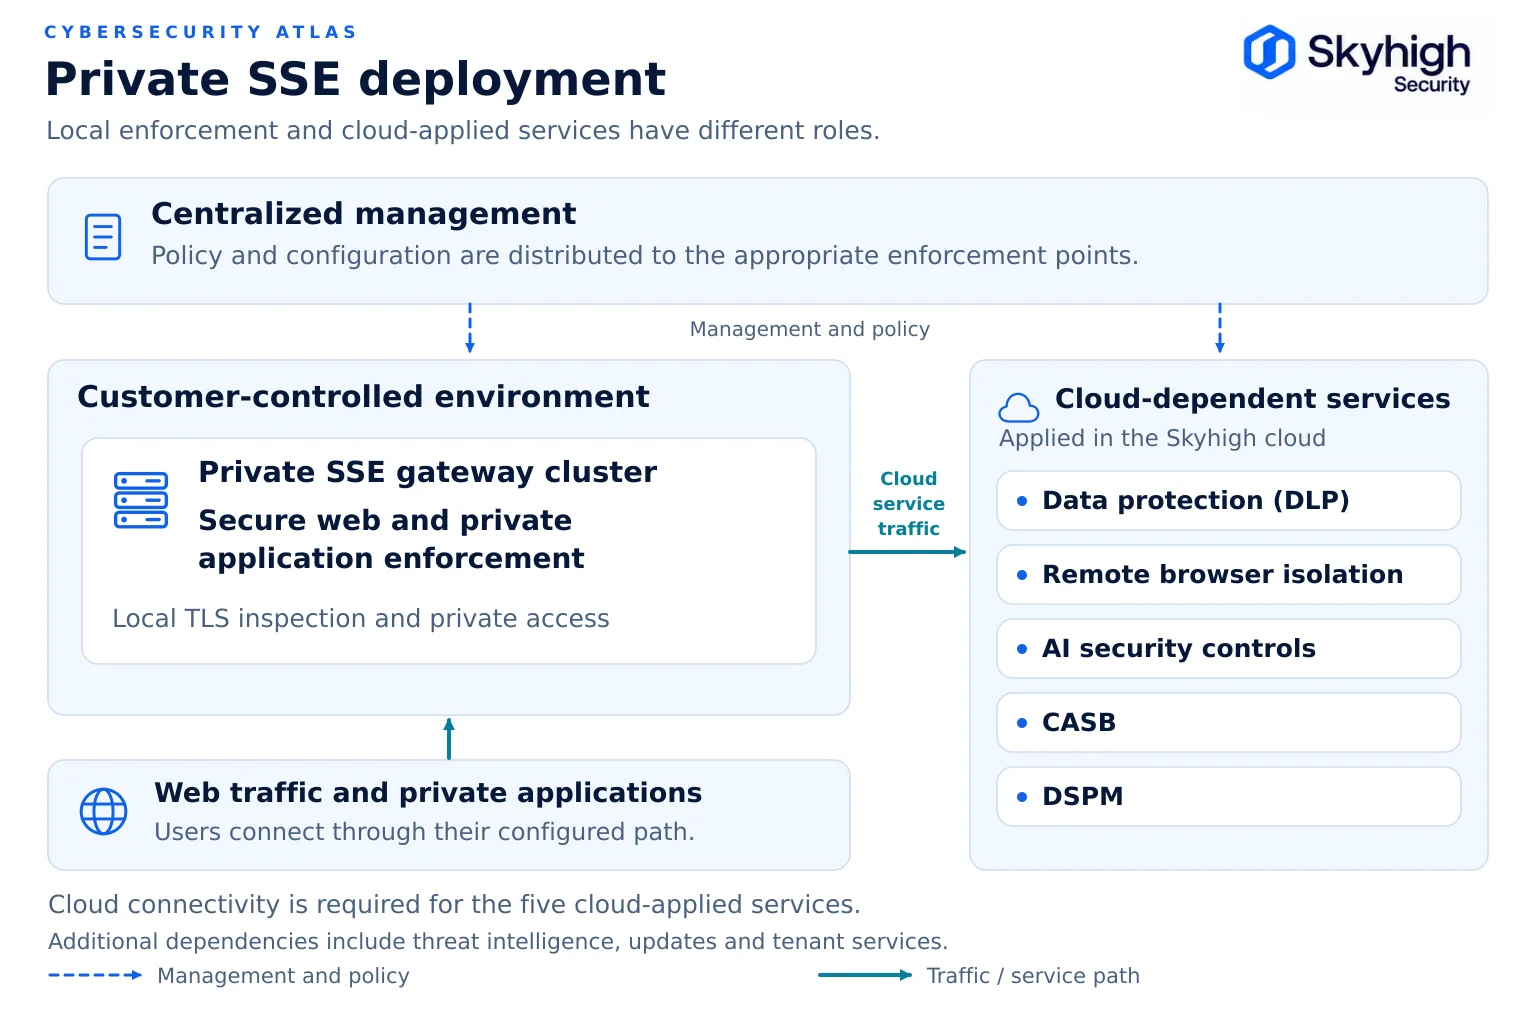
Enterprises choose Skyhigh because it keeps the data plane local where required, carries CPL policy forward, and extends to full SSE from one console.
Skyhigh Hybrid SSE Mesh unifies on-premises SWG appliances, local ZTNA, and Secure Browser Controls with cloud CASB, DSPM, DLP, and RBI under a single console. Web and private-access enforcement can run on premises, with TLS decryption and web inspection local; relevant traffic is forwarded for cloud-applied services. Existing CPL policies are re-expressed in Skyhigh’s unified policy console and validated before cutover, so teams start from their current policy state rather than a blank page.
Skyhigh was ranked first in the Advanced SSE Use Case in the 2026 Gartner® Critical Capabilities for Security Service Edge. More than 3,000 organizations use Skyhigh, including 80 percent of the largest global banks and nearly half of the Fortune 100, and the platform reports 99.999% uptime protecting more than 20 million users. It holds FedRAMP High authorization.
The Blue Coat Modernization Program applies remaining Broadcom investment toward the transition and pairs it with a guided, phased migration.
Next step: See the Symantec Edge SWG modernization overview or request a modernization assessment.
Sources
- Broadcom. End of life and product lifecycle for Edge SWG (ProxySG) and Advanced Secure Gateway (KB 151102). https://knowledge.broadcom.com/external/article/151102/end-of-life-and-product-lifecycle-for-pr.html
- Broadcom. Switch to the Edge SWG (ProxySG) Admin Console (SGAC) (KB 251426). https://knowledge.broadcom.com/external/article/251426/switch-to-the-edge-swg-proxysg-admin-con.html
- Broadcom. Web Isolation On-premises EOL FAQ (KB 215429). https://knowledge.broadcom.com/external/article/215429/web-isolation-onpremises-eol-faq.html
- Broadcom. Documentation for End of Life ProxySG. https://techdocs.broadcom.com/us/en/symantec-security-software/web-and-network-security/edge-swg/legacy/documentation-for-end-of-life-proxysg.html
- Skyhigh Security. “Modernizing Your Symantec Edge Secure Web Gateway With Skyhigh Hybrid SSE Mesh” (July 15, 2026). https://www.skyhighsecurity.com/industry-perspectives/modernizing-your-symantec-edge-secure-web-gateway-with-skyhigh-hybrid-sse-mesh.html
- Skyhigh Security. Modernize Symantec Edge SWG (Blue Coat). https://www.skyhighsecurity.com/bluecoat-modernize.html
- Skyhigh Security. “Skyhigh Security Ranked #1 in Advanced SSE Use Case in 2026 Gartner Critical Capabilities for Security Service Edge” (August 5, 2026). https://www.globenewswire.com/news-release/2026/08/05/3339504/0/en/skyhigh-security-ranked-1-in-advanced-sse-use-case-in-2026-gartner-critical-capabilities-for-security-service-edge.html
GARTNER is a registered trademark and service mark of Gartner, Inc. and/or its affiliates in the U.S. and internationally and is used herein with permission. All rights reserved. Gartner does not endorse any vendor, product or service depicted in its research publications.