Resources
Securing the New Normal: Why Universal Zero Trust is Essential in the Age of AI
By Sriram Krishnamurthy - VP, Engineering
September 30, 2026 4 Minute Read

The security landscape is shifting rapidly, and the rules of engagement have changed. We have entered an era where AI-powered tools like “Mythos” are not just theoretical concepts; they are operational realities. These tools can autonomously identify vulnerabilities, exploit unpatched systems, and navigate internal networks with unprecedented speed and precision.
It is critical to state that a strong preventive strategy remains the bedrock of any security posture. Organizations must continue their due diligence in keeping systems updated, hardening configurations, and maintaining rigorous patch management cycles. This new reality introduces a relentless operational burden causing significant gaps in the process forcing us into impossible positions:
- The Patching Treadmill: The window of opportunity to remediate vulnerabilities has shrunk to near zero. Security teams are now forced into a cycle of “immediate patching” the moment a security update is released, creating an unsustainable operational strain.
- Vendor Dependency: We are effectively at the mercy of software vendors to maintain rigorous, secure development lifecycles. Even with the best intentions, a single delay in a vendor’s patch release leaves a gaping hole that an AI tool can exploit in seconds.
- The Zero-Day Threat: Perhaps most concerning is the ability of AI tools to discover and weaponize zero-day vulnerabilities in real-time, bypassing traditional defenses that rely on known signatures or patterns.
Relying solely on a preventive strategy—doing due diligence and patching regularly—is no longer sufficient. While those practices remain critical, they must be backed by a pragmatic, comprehensive risk mitigation approach. We must accept that intrusions are inevitable and prepare to handle them with an effective, resilient strategy.
The Failure of the “Castle-and-Moat”
For years, the “castle-and-moat” model was the standard. Organizations focused on blocking intrusions at the network edge, trusting everything inside the perimeter. This created a flat, trusted network where attackers could easily move laterally once the perimeter was breached.
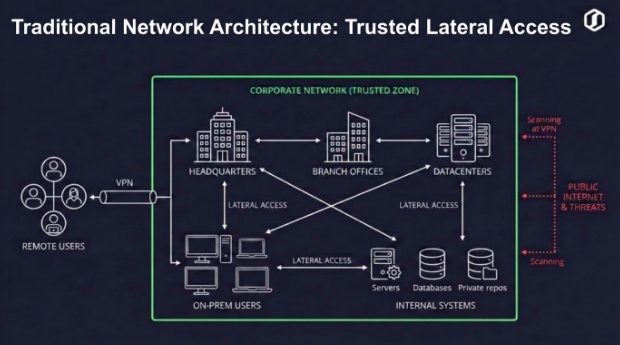
Traditional VPNs, long the go-to for remote access, have only compounded this issue. They essentially “punch a hole” in the network, granting broad access through a tunnel. Even with firewall rules in place, these systems lack context of the applications, users and endpoint devices and how they interact with each other, making it nearly impossible to manage policies effectively against dynamic network changes.
Furthermore, traditional methods like VLAN segmentation have proven inadequate. An attacker who compromises a single endpoint within a VLAN gains full access to other systems, allowing them to move laterally toward your most critical assets. In an age where AI-driven penetration tools can quickly scan for these weak points and craft attack vectors, the old way of doing things is no longer sustainable.
The Shift to Universal ZTNA
To effectively counter the threats of lateral movement and AI-driven exploitation, organizations must move beyond legacy defenses. This is where Universal Zero Trust Network Access (ZTNA) provides the critical architecture needed for modern security.
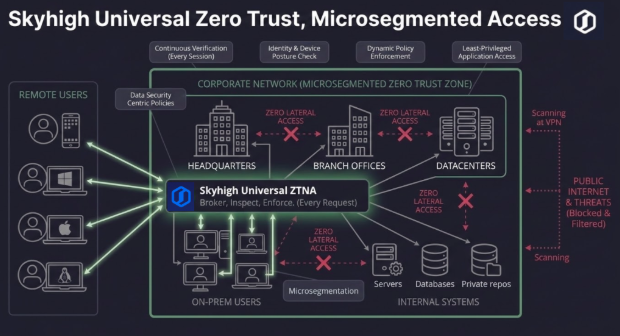
Universal ZTNA is more than just a remote access tool; it is an architectural shift that enforces consistent, least-privilege security policies for every user, every device, every application and every interaction between them, regardless of whether they are working from home, a branch office, or headquarters. The security shifts from “network-centric” to “application-centric.”
How Skyhigh’s Hybrid Mesh SSE Platform Changes the Game
Skyhigh Security’s Hybrid Mesh SSE platform delivers a modernized, layered approach to security with the following Universal ZTNA capabilities:
- No More Open Tunnels: Unlike VPNs, ZTNA eliminates the need to set up tunnels into the corporate network. Instead, the ZTNA Connector establishes an outbound connection to the SSE Cloud, where policies are enforced. If traffic isn’t explicitly allowed by the administrator, it never touches the network.
- Micro-segmentation: We move security from macro-level VLAN segmentation to micro-segmentation. By intercepting east-west traffic from every endpoint, blocking it by default and allowing only based on access policies defined by the Security team, we make lateral movement nearly impossible, even if a single endpoint is compromised.
- Continuous Verification: Security is not a one-time event. Our client continuously evaluates device posture and can revoke access in real-time if a risk is detected mid-session.
- Local Zero Trust: The challenge with Universal Zero Trust delivered exclusively in the cloud is that it causes friction for local users accessing local applications and workloads as users are forced out to the cloud for Zero Trust validation and enforcement, only to ‘Hairpin’ right back to an application that might be located right next to them. This leads to increased latency and compromised data sovereignty. Skyhigh Security’s Hybrid Mesh SSE platform addresses this by ensuring policy Zero Trust enforcement for on-prem traffic is done on the local network.
- Data Security Centric Policies: Firewalls are blind to data exfiltration within an “authorized” network. Universal ZTNA integrates with Skyhigh DLP and Secure Web Gateway (SWG) to inspect data, ensuring that sensitive information remains secure even if it’s being handled by a “trusted” internal user.
- Defense in Depth: ZTNA is not an isolated product. It is a network architecture that integrates your existing ecosystem with several security solutions, such as IAM, Skyhigh’s Gateway Anti-Malware (GAM), Skyhigh Data Loss Prevention & Data Security Posture Management, Remote Browser Isolation (RBI) and Skyhigh Secure Browser Controls—to create a secure, cohesive, resilient fabric.
The Cost of Doing Nothing
Research shows that while most organizations are aware of these threats, many fall into the trap of wishing and hoping they aren’t the next target. There are few organisations who thoroughly understand the risks and fewer who work on the right security controls to stay safe. In reality, a compromise is a business showstopper, leading to massive financial loss and reputation damage.
Universal ZTNA isn’t just an upgrade; it is a future-proof foundation. By adopting this framework, you move beyond the limitations of legacy networks and build a posture that is as agile and sophisticated as the AI-powered threats we face today.
Is your network architecture ready for the age of AI? Download our whitepaper on Universal ZTNA or contact our team for a personalized risk assessment.
About the Author
Sriram Krishnamurthy
VP, Engineering
Sriram is VP of Engineering at Skyhigh Security who brings over 25 years of experience architecting, building, and scaling cutting-edge security solutions.
Related Content
Securing the New Normal: Why Universal Zero Trust is Essential in the Age of AI


Trending Blogs
Securing the New Normal: Why Universal Zero Trust is Essential in the Age of AI
Sriram Krishnamurthy September 30, 2026
Work is Hybrid. Why Are You Paying Double for a Cloud Tax on the Office?
Mike Smart September 24, 2026
We Can’t Stop the AI Race. We Can Make It Safer and More Secure.
Thyaga Vasudevan September 15, 2026
AI Is Changing Your Data Risk. DSPM Puts You Back in Control.
Megha Shukla September 4, 2026
Why Customers Love Mowgli: The IKEA Effect in Cybersecurity
Thyaga Vasudevan August 13, 2026








