Zero Trust Where Work Happens
Extend Zero Trust Inside The Office
The Zero Trust promise must reach inside the organization, not stop at the cloud edge. In-office users, AI agents, internal applications and AI workflows need controls closer to where work is done.
The In-Office Blind Spot
Cloud-Only Zero Trust Stops at The Edge
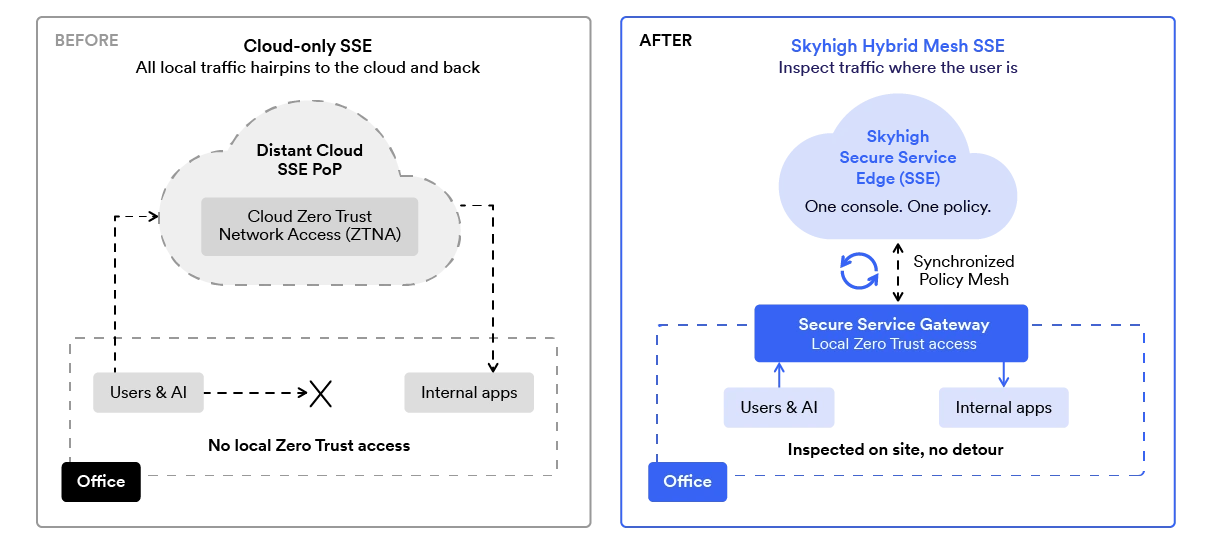
Zero Trust that stops at the cloud edge isn’t Zero Trust at all. Cloud-only Zero Trust Network Access (ZTNA) introduces latency and fails to enforce access for internal, East/West traffic. Security must follow where work happens, not force your workflows to fit a vendor’s cloud architecture.

Network Access is Not Application Access
Cloud-delivered ZTNA does exactly what it says, it was designed to provide Zero Trust access for remote users to the local network. Unfortunately it typically does not provide Zero Trust access to each private application. This deficiency is exacerbated when local users access local applications. Not only does their traffic get hairpinned to the cloud, their local East/West traffic is also not monitored.

The Local AI Gap
Users and machine-speed AI agents operate inside your perimeter. Cloud proxies providing network access cannot inspect local flows, exposing sensitive data to unmonitored LLM prompts. Only Zero Trust enforced locally combined with advanced data protection can close the In-office AI gap.
Skyhigh Hybrid Mesh SSE
Zero Trust Access Everywhere.
Skyhigh Security Hybrid Mesh SSE decouples control from enforcement. Author your security policy once and enforce it locally on customer-controlled Secure Service Gateways or in the cloud based on workflow requirements.

Local Zero Trust Access
Contain lateral movement inside the network. Deliver Zero Trust for local users, contractors, and internal application access without backhauling traffic unnecessarily through external Cloud SSE infrastructure.

Inline AI & Data Security
Prevent sensitive enterprise data, source code, and customer records from leaking into GenAI prompts. Enforce agentless browser controls, prompt DLP, and web inspection for local AI traffic.

Unified Policy‑as‑Code
Eliminate multiple administration consoles. Governed by Skyhigh’s policy-as-code engine, security rules are consistently enforced across local appliances, virtual gateways, and cloud PoPs.
Get Zero Trust Everywhere
Book a custom assessment to see how enforcing security where work actually happens can modernize your security architecture and more efficiently secure your In-office users, contractors, internal apps, and AI agents.
Your Next Steps To Zero Trust Everywhere
A Practical Path to Hybrid Security Without Migration Risk
Expand your on-premises security capabilities and right-size your cloud SSE investments to where your employees work and your data and AI flows.

Modernize On-Premises Web Security
Upgrade your aging on-premises web security technologies into modern Secure Service Gateways capable of inspecting and enforcing SSE services, like Zero Trust access, locally on each network.

Extend SSE Services With Local Control
Expand the use of additional advanced cloud SSE capabilities, including Cloud Access Security Broker (CASB) and Remote Browser Isolation (RBI) at your own pace without surrendering local control.

Unify Hybrid Telemetry & Visibility
Eliminate blind spots between cloud and local networks by feeding all access events, DLP incidents, and user risks into a single reporting console.

Migrate Existing Policies
Our professional services team work with you to review, optimize and migrate your policies for existing on-premises web gateways and cloud SSE products.
ทรัพยากร
Learn More About Zero Trust Everywhere
 อ่านเพิ่มเติมData Sheet
Symantec Edge SWG Modernization Brief
 อ่านเพิ่มเติมบล็อก
Work is Hybrid. Why Are You Paying Double for a Cloud Tax on the Office?
 อ่านเพิ่มเติมแท่น
Hybrid Mesh SSE
- อ่านเพิ่มเติมสารละลาย
Cut Web Security & SSE OPEX with Hybrid Mesh SSE
- อ่านเพิ่มเติมสารละลาย
Data Sovereignty & Resilient SSE Solutions
-
 อ่านเพิ่มเติมวิดีโอ
Skyhigh DSPM Video Demo
-
 อ่านเพิ่มเติมData Sheet
Skyhigh Client & Mobile Client
-
 อ่านเพิ่มเติมบทสรุปโซลูชัน
Operationalizing DSPM: Five real-world use cases for data-centric security
-
 อ่านเพิ่มเติมการสัมมนาผ่านเว็บ
Closing the Browser Security Gap: Hidden AI Cybersecurity Risks
-
 อ่านเพิ่มเติมWhite Paper
Turning Data Visibility into Enterprise Protection
-
 อ่านเพิ่มเติมการสัมมนาผ่านเว็บ
Work Is Hybrid. Why Isn’t Your Security?
-
 อ่านเพิ่มเติมบทสรุปโซลูชัน
Skyhigh Secure Browser Controls: In-Session Data Protection for Every Browser and Device
-
 อ่านเพิ่มเติมบทสรุปโซลูชัน
Skyhigh Secure Browser Controls Buyer’s Guide
Next Steps
Put Zero Trust Where Work Actually Happens
Schedule time with one of our experts to assess your environment, compliance requirements, and AI security needs.